


The Operational Challenge of PP 33/2026: Maintaining Privacy Compliance Across the Organization
Learn how to sustain data protection compliance under PP 33/2026, with insights from Cisometric's DPO on vendor risks, privacy controls, and...
By Cisometric, Published on May 15, 2025
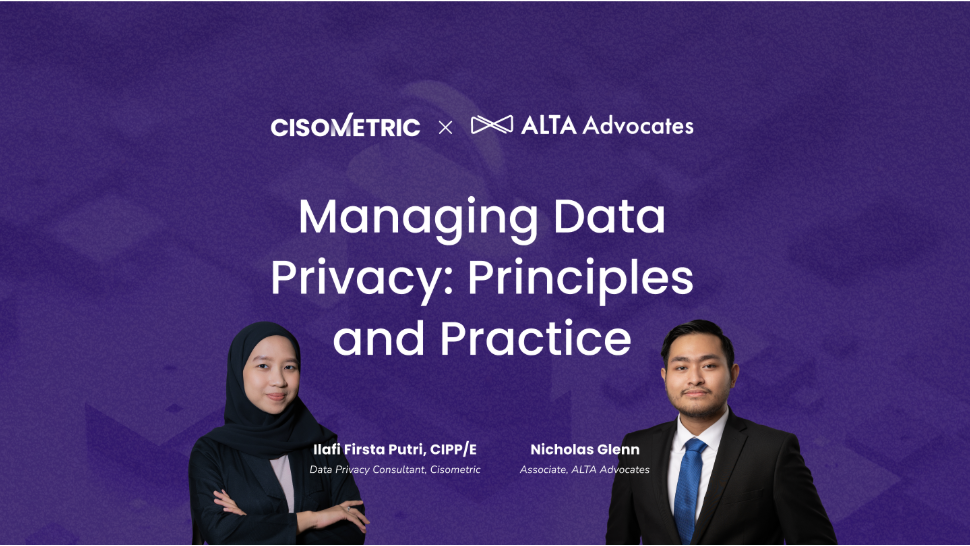
On May 7, 2025, Cisometric, in collaboration with ALTA Advocates, welcomed professionals from across legal, compliance, and IT security fields to our first #CyberTalks session of the year: Managing Data Privacy: Principles and Practice.With data privacy becoming a core concern for companies operating in Indonesia, the session was designed to answer one big question: What does it really take to comply with the Personal Data Protection Law (UU PDP)?Take it from us, it’s more than just ticking compliance checkboxes, it involves reshaping how organizations approach both governance and technology.
What rights data subjects are entitled to
The importance of appointing a DPO (Data Protection Officer)
How to maintain ROPA (Records of Processing Activities)For many attendees, this session served as a much-needed crash course in what the law actually requires, and how to start assessing whether their current processes measure up.
What a compliance roadmap looks like from a technical perspective
Where tools and technologies can step in to automate, support, and document privacy efforts
The opportunities and challenges of using privacy tech in real-world settingsIlafi’s message was clear: compliance can’t just sit in the legal department. IT, compliance, and leadership all have to work together. And with the right frameworks like ISO 27701 in place, the road to PDP readiness becomes much more structured.
What kind of internal system is needed for compliance?
Are there tools that can help automate data subject requests or consent management?It was clear that the audience wasn’t just curious, they were looking for practical answers they could take back to their teams.
This #CyberTalks forum gave us a front-row seat to where many organizations currently stand in their data privacy journey in Indonesia, and just how much demand there is for guidance, clarity, and collaboration.We’re incredibly grateful to our speakers and attendees who helped make this event so valuable. These conversations are just the beginning, and we’re excited to continue supporting companies as they navigate compliance and build stronger, privacy-aware systems.Stay tuned for our next #CyberTalks. We’re just getting started.Follow our social media to get the latest updates on upcoming sessions, expert insights, and cybersecurity resources tailored for your organization.Follow us on:LinkedIn: CisometricInstagram: @cisometricYoutube: Cisometric
Learn how to sustain data protection compliance under PP 33/2026, with insights from Cisometric's DPO on vendor risks, privacy controls, and...
PP 33/2026 takes effect on 16 January 2027. Discover the compliance gaps organizations must address now, with expert insights from Cisometri...
On 9 July 2026, Cisometric, in collaboration with ISACA Indonesia Chapter, gathered professionals from banking, fintech, risk, compliance, a...
Search Article by Category
We use cookies to enhance your browsing experience, analyse site traffic, and deliver relevant content. Choose which cookies you allow. Privacy Policy