Before the Incident: How Cisometric DevSecOps Builds SOC Response Readiness
Learn how DevSecOps strengthens SOC incident response readiness through better telemetry, system context, access, playbooks, and upstream se...
By Cisometric, Published on October 7, 2026
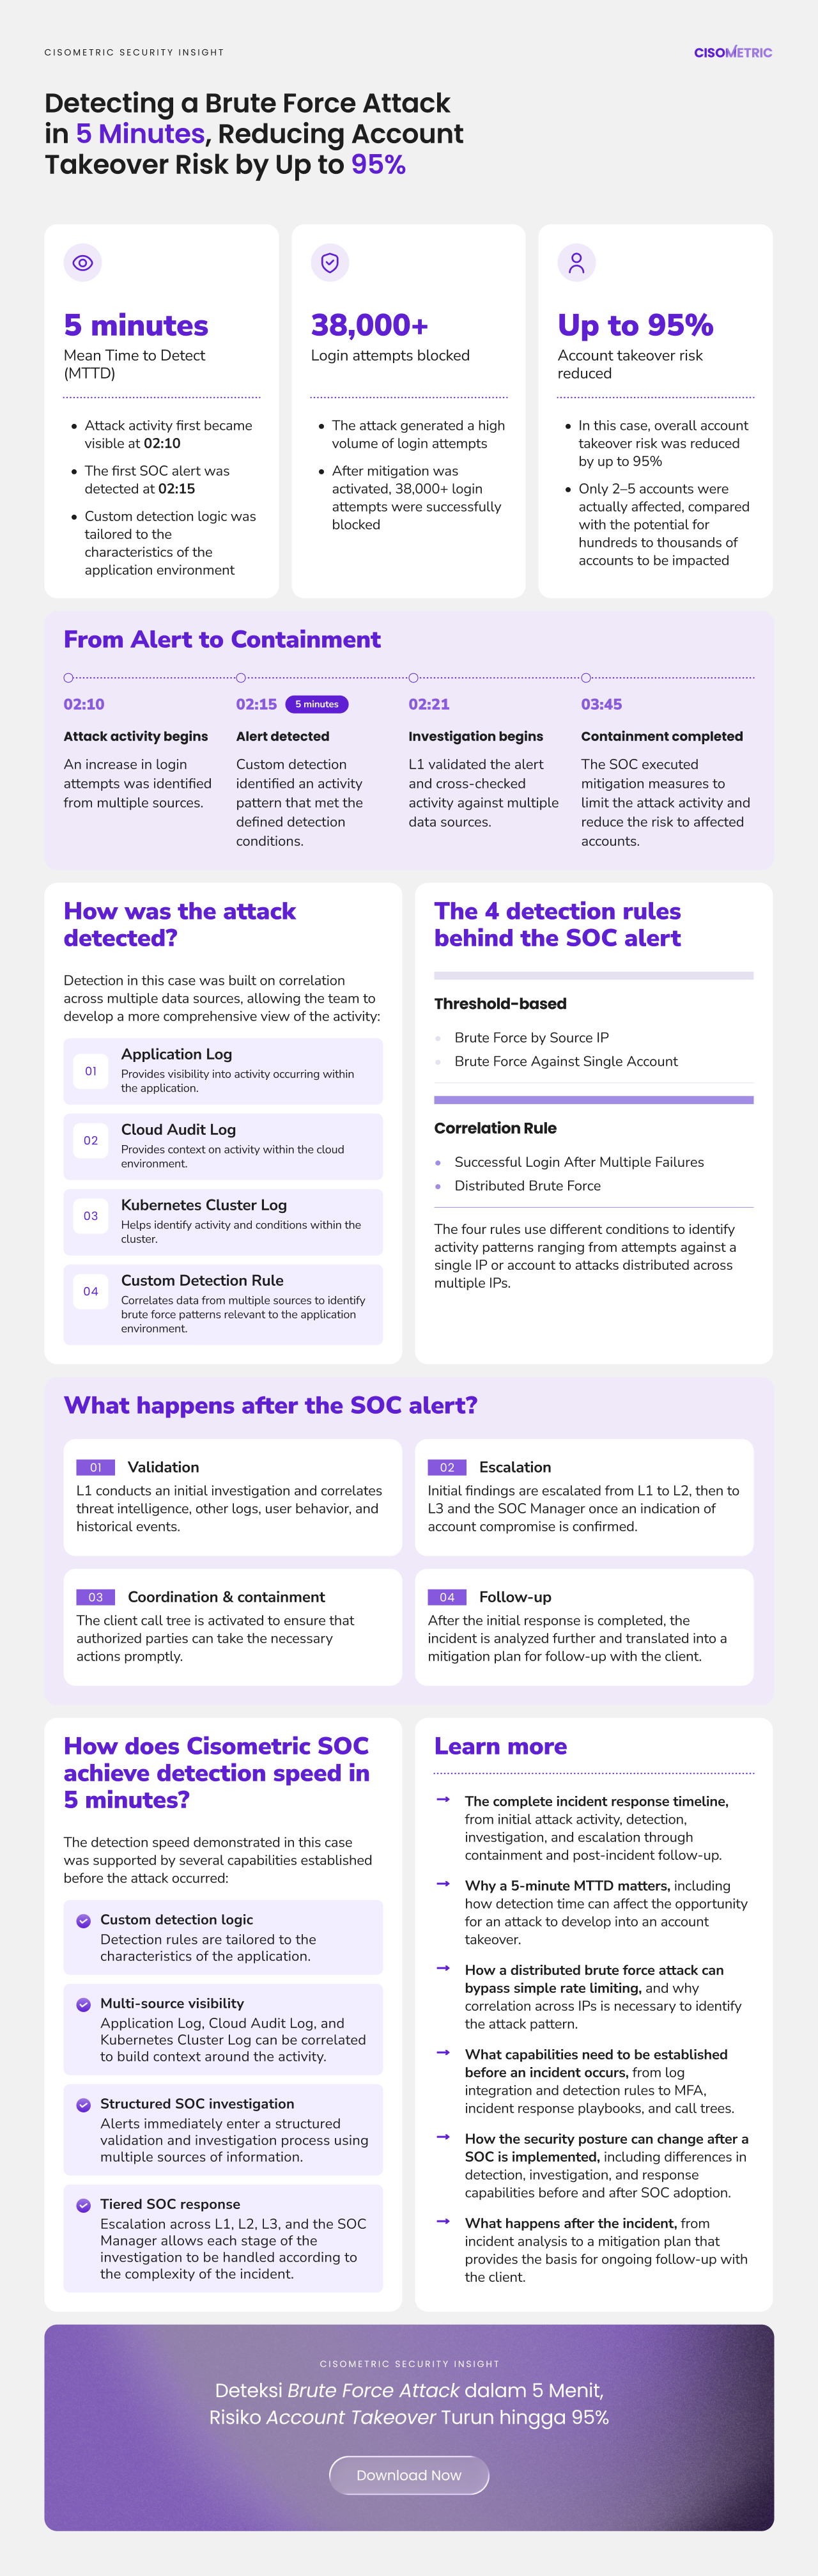
Brute force attacks can generate thousands of login attempts within a short period. When such activity targets a public-facing application with tens of thousands of daily users, the sheer volume of events and distributed attack patterns can make detection and investigation increasingly complex.
In this white paper, Cisometric examines how a distributed brute force attack was detected, investigated, and handled by a SOC team. The attack activity first became visible at 02:10, while the first alert was detected at 02:15, resulting in a Mean Time to Detect (MTTD) of 5 minutes. The team then proceeded with investigation, escalation, and containment.
So, what happened between those five minutes and containment?
Learn how DevSecOps strengthens SOC incident response readiness through better telemetry, system context, access, playbooks, and upstream se...
Explore how AI-powered threats are changing attack speed, scale, and autonomy, and what SOC teams need to strengthen detection, investigatio...
Panduan teknis CTI: 3 tingkatan CTI, klasifikasi stealer logs vs combolists, Scattered Spider help desk bypass, IMDS cloud, dan kepatuhan UU...
Search Article by Category
We use cookies to enhance your browsing experience, analyse site traffic, and deliver relevant content. Choose which cookies you allow. Privacy Policy